
Router Proxy Firewall Explained: Roles, Setups, and Uses

A Router Proxy Firewall may sound like a single product, but it isn't. It refers to different ways of combining 3 network functions, each with its own role. This guide explains how routers, proxies, and firewalls differ, how they work together, and which setup makes sense for your network. You'll also find a simple setup guide to help you get started.
What Is a Router Proxy Firewall?
Router Proxy Firewall isn't a standardized product category. Depending on the context, it can refer to one of several network arrangements:
Separate components: A router, proxy server, and firewall perform their own tasks while working within the same network.
A router with an external proxy: The router and firewall manage local traffic, while a separate proxy provides another path to the internet.
An all-in-one gateway: One device handles routing, proxy connections, and traffic filtering.
A proxy firewall: The firewall acts as an intermediary, creating separate connections while inspecting the traffic passing through it.
These arrangements may use similar functions, but they process traffic differently. Identifying which setup the term refers to makes it easier to understand the network and choose the right configuration.
Router, Proxy, and Firewall at a Glance
Routers, proxies, and firewalls all manage network traffic, but they do so for different reasons. A router directs traffic, a proxy forwards requests on behalf of a device, and a firewall decides which traffic is allowed to pass.
Router | Proxy | Firewall | |
Definition | Connects networks and directs traffic | Relays requests for a client | Filters traffic using security rules |
Core role | Send traffic to the right destination | Route traffic through another server | Allow or block network traffic |
Traffic handling | Forwards data using routing rules | Connects clients indirectly to destinations | Inspects traffic before allowing it through |
Public IP | Uses the network's public IP | Shows the proxy server's IP | Usually does not change the public IP |
Security role | May include NAT and basic firewall protection | Adds separation but does not replace a firewall | Protects against unauthorized traffic |
Advantages | Connects devices and manages local traffic | Provides IP and location flexibility | Enforces access and security policies |
Limitations | Limited IP and location control | May reduce speed and adds no complete protection | Provides no proxy IP flexibility |
Common uses | Home networks, offices, and internet sharing | IP management and location-based access | Access control and threat prevention |
How Do Router, Proxy, and Firewall Work Together?
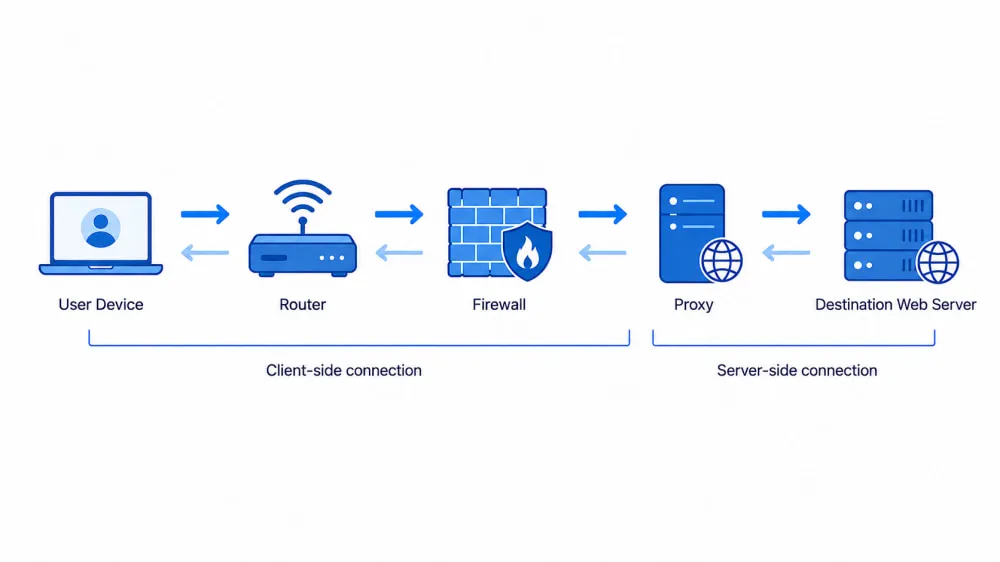
The diagram below shows how the 3 components can handle the same traffic while performing different tasks. The router decides where the traffic goes, the firewall determines whether it can pass, and the proxy forwards allowed requests on the client's behalf. Routing, filtering, and proxying remain separate actions, even when one device performs all three.
A proxy firewall may terminate the client connection and open a separate connection to the destination. It therefore handles two distinct connections: client to proxy firewall and proxy firewall to destination. Firewall controls may be placed before the proxy, after it, on either side, or integrated with the proxy. The exact arrangement depends on the devices, configuration, and network architecture.
Router, Proxy, and Firewall Setups: When to Use Each
Router, proxy, and firewall functions do not have to live in the same box. A network can rely on a router's built-in protection, add an external proxy, or bring all three functions into one gateway. The best choice comes down to how much control you need over security, outgoing IPs, and network administration.
Router With a Built-In Firewall
Most routers already do two jobs. They connect devices and direct traffic, while a basic firewall screens what enters or leaves the network. It typically rejects unsolicited inbound connections by default.
For many home and small office networks, that is enough. It keeps things simple and provides basic protection without another service to configure. What it cannot do is route traffic through a different public IP or change how websites see your network location.
Router With an External Proxy
An external proxy adds control over the outgoing connection without replacing the router or firewall. The router continues moving traffic between networks, and the firewall applies its rules as usual. Selected traffic then passes through the proxy, which connects to the destination using its own IP address.
This arrangement works when multiple devices need the same proxy IP or centralized proxy management. On a compatible router, one configuration can route supported traffic through a fixed endpoint, avoiding device-by-device setup and keeping the visible IP consistent. Coverage depends on protocol support and routing rules, while proxied traffic may stop if the endpoint fails.
IPcook fits this arrangement with reliable performance and straightforward authentication. Its ISP Proxies are well suited to stable, long-term router use, offering a fixed endpoint, 99.9% uptime, unlimited traffic, and low latency. Plans start at $0.05 per IP per day. Each proxy comes with an IP address and port, plus a username and password for authentication. If the router setup is intended for enterprise-scale web scraping, IPcook Datacenter Proxies are the more suitable option. Both proxy types support HTTP and SOCKS5 protocols.
All-in-One Router Proxy Firewall
At the other end of the spectrum is an all-in-one gateway. It handles routing, proxy connections, and firewall policies within one device or software platform. Traffic rules, proxy settings, access controls, and network activity all sit in the same management interface.
The appeal is centralized oversight. Policies are easier to apply consistently when the whole traffic path is managed in one place. Still, a single interface does not necessarily mean a simple deployment. These systems usually demand more planning and technical knowledge than a standard router.
💡You May Like:
How to Set Up a Router Proxy Firewall
Router menus and capabilities vary widely. These steps use an external proxy because it adds centralized proxy access without replacing the existing router or firewall. On a compatible router, one configuration can cover supported traffic from multiple devices. Below is a simple setup guide using IPcook as an example.
Check compatibility: Make sure the router or gateway supports an upstream HTTP or SOCKS5 proxy.
Get a proxy: Choose an IPcook ISP Proxy for a fixed, stable endpoint or a Datacenter Proxy for enterprise-scale scraping. Copy the IP address, port, username, and password.
Configure the router: Find the proxy settings in the router's admin panel, select the correct protocol, and enter the IPcook proxy details. Keep the firewall enabled and allow outbound connections to the proxy IP and port.
Test the connection: Check the visible IP from a connected device. If it does not match the proxy IP, review the protocol, port, credentials, and firewall rules.
💡Related Reading:
IPcook User Guide: A Quick Start to Proxy Setup and Configuration
Summary
A Router Proxy Firewall is not always one product. It may describe a router with built-in protection, a router connected to an external proxy, or an all-in-one gateway. The router directs traffic, the firewall filters it, and the proxy relays selected connections. The right arrangement depends on the level of IP and security control you need. For external proxy setups, IPcook offers stable ISP Proxies and Datacenter Proxies for enterprise-scale scraping, both with HTTP and SOCKS5 support.